From CVE data to priorities in minutes – Built for networks where security can’t rely on manual checks
BECS Security Module brings a new approach to network vulnerability management as the first solution to automatically match network hardware and firmware against known CVEs across multi-vendor environments. It gives you one place to identify relevant vulnerabilities, understand what may be affected and prioritise where your attention is needed.
 Turn days of manual research into minutes
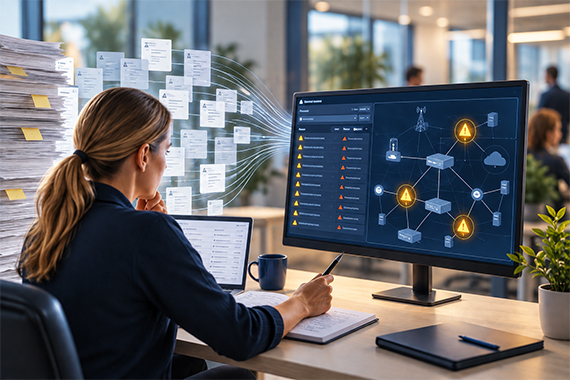
Reviewing CVE databases is only the beginning. Manually working out which CVEs are relevant to your network, matching them to your hardware and firmware, keeping track of the findings and deciding what needs attention first can sometimes take hours, or even days.
BECS Security Module automates that process. Vulnerability data is retrieved twice daily from one of the world’s largest CVE databases and automatically matched against your registered network infrastructure.
Instead of searching, cross-referencing and maintaining separate lists, you can quickly see known CVEs relevant to your network and focus your time on reviewing and prioritising the findings.
 One view across your network environment
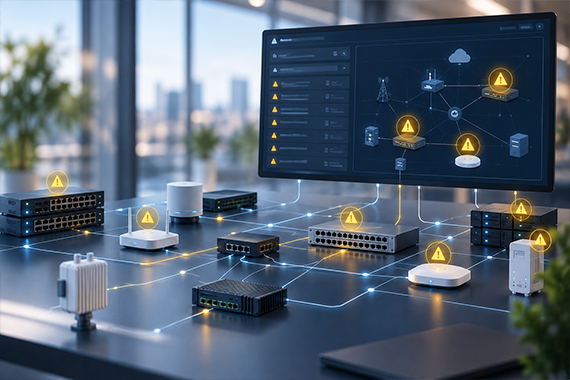
Whether your network is built around a single vendor or multiple vendors, BECS Security Module brings relevant CVE information together in one place.
You can see which known CVEs affect your registered devices, review and sort the findings, and quickly understand where vulnerabilities exist across your network infrastructure.
This means less time spent finding and organising vulnerability information, a lower risk of overlooking known CVEs and better information for deciding what requires attention first.
Built for networks where security can’t rely on manual checks
BECS Security Module is designed for telecom operators and other organisations managing network infrastructure where keeping track of known firmware vulnerabilities is an ongoing responsibility. As networks grow, and the number of devices and firmware versions increases, manually checking and maintaining CVE information becomes increasingly difficult to manage.
Start with Security Module
Already using BECS? Security Module adds vulnerability intelligence directly to your existing network management environment.
New to BECS? You can start with Security Module without undertaking a full BECS implementation. This gives you a lighter way to introduce automated vulnerability monitoring to your network without implementing the wider capabilities of the BECS platform.
 From visibility towards remediation
BECS Security Module starts by helping you identify and more easily prioritise known vulnerabilities. Future versions are planned to extend that capability with firmware upgrades, taking the journey further from vulnerability identification towards remediation.
Release webinar 13 October
BECS Security Module
At the release webinar, we’ll take a closer look at BECS Security Module, and how it can help you identify known vulnerabilities across single and multi-vendor network environments. See how CVE data is automatically matched against your network hardware and firmware, turning hours or even days of manual research into minutes and helping you focus on what needs attention first.
🕐 Time: 14:30 – 15:00. (CET)
👉 Join the release webinar by signing up here: BECS Security Module release webinar>>
Explore our 2026 event line-up

We’ll be out and about again in 2026. Come and see where you can catch us: Explore our 2026 event line-up>>
Stay on top – Get the latest news from PacketFront
 Get the latest news on upcoming features, solutions and products, plus invitations to our courses and events. Subscribe here>>